By The Pulseline News Desk
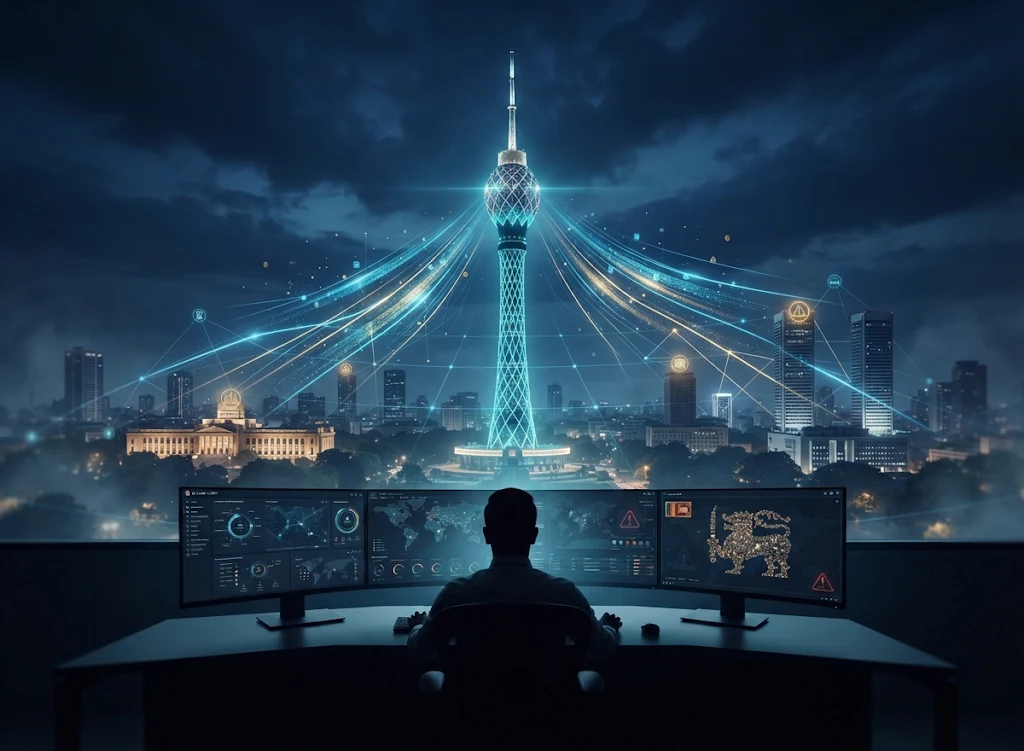
Sri Lanka is moving towards enacting a long-awaited Cybersecurity Act in early 2027, paving the way for the establishment of a dedicated authority with powers to regulate cybersecurity standards, conduct mandatory audits and oversee the protection of critical digital infrastructure.
Deputy Minister of Digital Economy Eranga Weeraratne has said the proposed legislation had reached its final stages, with the latest draft revised by the Legal Draftsman’s Department and forwarded to the Attorney General’s Department for observations in October 2026.
The legislation is expected to establish a permanent legal framework for addressing cyber threats, including provisions requiring organisations operating in critical sectors to report security incidents, undergo cybersecurity audits and implement corrective measures.
Sri Lanka has been attempting to introduce comprehensive cybersecurity legislation since 2019, but successive drafts failed to reach the implementation stage.
Weeraratne has said the latest initiative was intended to end years of delays and provide the country with a stronger institutional and legal framework to respond to an increasingly complex cyber threat environment.
Expanding government cyber surveillance
Alongside the legislative process, the Government is expanding its monitoring of public sector digital infrastructure.
Sri Lanka CERT currently conducts continuous security scans of internet-facing systems belonging to 150 government organisations, including institutions responsible for critical infrastructure. The programme is expected to cover more than 250 institutions next year.
The National Cybersecurity Operations Centre (NCSOC) is also providing real-time monitoring of connected government networks to identify suspicious activity and issue early warnings of potential cyber threats.
The Cabinet has directed 37 Chief Information Officers across government institutions to connect their organisations to the NCSOC by December 31, 2026.
So far, 17 institutions have been integrated into the system. These include the President’s Office, Prime Minister’s Office, Parliament, Ministry of Finance, Ministry of Foreign Affairs, Department of Examinations, Telecommunications Regulatory Commission, Attorney General’s Department and Legal Draftsman’s Department.
The National Water Supply and Drainage Board and several airport and aviation-related institutions have also been connected.
With assistance from the Asian Development Bank (ADB), the Government plans to extend NCSOC coverage to as many as 150 organisations by 2029.
Limits of existing cybersecurity powers
Weeraratne has explained that Sri Lanka CERT currently plays a central technical role in identifying cyberattacks, monitoring vulnerabilities and alerting affected institutions.
However, its mandate does not extend to regulatory or enforcement decisions, such as freezing financial transactions or directing institutions to take measures requiring specific legal authority.
The proposed Cybersecurity Authority is expected to address part of this institutional gap by providing a dedicated regulatory structure with powers established under legislation.
Government defends decision on cyber risk disclosures
The Deputy Minister has also defended the Government’s decision not to publish detailed national cybersecurity risk assessments, arguing that public disclosure could expose vulnerabilities in critical digital infrastructure.
He has said releasing detailed assessments of weaknesses in government systems could provide potential attackers with information about the country’s most vulnerable digital assets.
While acknowledging the importance of transparency, Weeraratne has maintained that sensitive cybersecurity assessments should not be made publicly available where disclosure could undermine national security.
Instead, the proposed legislation is expected to establish formal accountability mechanisms.
The new Cybersecurity Authority will be required to submit annual reports to Parliament, while existing parliamentary oversight committees will retain the authority to summon officials and examine its operations.
If enacted as expected in early 2027, the legislation would mark a major shift from Sri Lanka’s largely institution-based approach to cybersecurity towards a legally backed regulatory system, with mandatory compliance requirements and parliamentary oversight.



Leave a comment